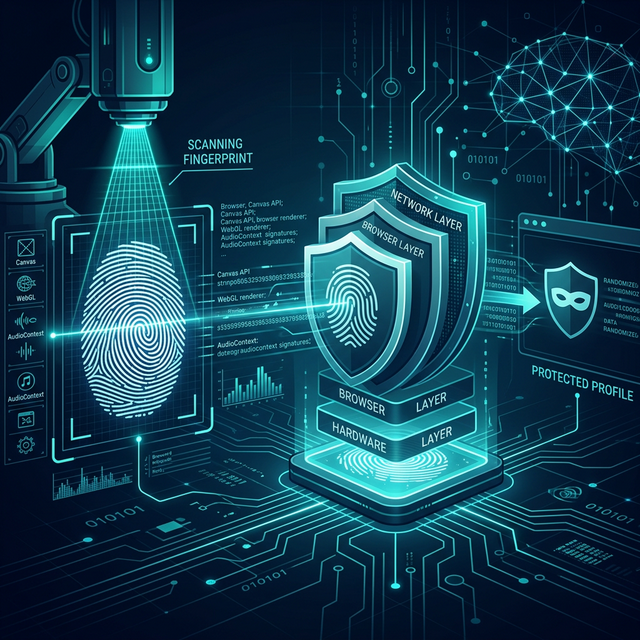
Antidetect VM (anti-detection virtual machine) is a VMware/VirtualBox machine that has been deeply hardened to erase every trace of virtualization — from CPUID, SMBIOS and MAC address to the browser fingerprint — so websites, ad platforms and anti-fraud systems can no longer tell that your environment is a "virtual machine". This guide explains why ordinary VMs get detected, how an undetectable virtual machine works, and when you should pick a VM instead of an antidetect browser.
Why Do Websites Detect Virtual Machines?
Every time you visit a website, dozens of signals are collected from your machine. A "bare" VMware machine leaks many telltale signs:
- CPUID & Hypervisor Bit — the CPUID instruction returns the "VMwareVMware" string and the hypervisor flag is on by default: the fastest detection method.
- SMBIOS/DMI Strings — the hardware table contains "VMware, Inc." as motherboard manufacturer and model.
- MAC Address OUI — VMware virtual NICs always start with the
00:0C:29prefix, which can be reverse-looked-up. - Registry & Processes — keys such as
SOFTWARE\VMware, Inc.\VMware Toolsand thevmtoolsd.exeprocess keep running inside the guest OS. - Timing Attacks — measuring RDTSC and VM-exit latency reveals the virtualized environment.
- Browser Fingerprinting — Canvas, WebGL, WebRTC, fonts and timezone all leak the virtual GPU and your real IP.
Result: accounts created on a stock VM risk mass bans because the platform detects that you are running a "virtual environment". That is exactly why the antidetect VM exists.
How Does an Antidetect Virtual Machine Work?
An undetectable virtual machine solves the problem at three layers:
1. Hypervisor Layer — Erasing VMware Traces
The .vmx file is configured to disable the 0x5658 backdoor port, remove the CPUID vendor string, reflect the real machine's SMBIOS (SMBIOS.reflectHost = TRUE) and hide all VMware Tools processes inside the guest. The guest OS then believes it runs on real hardware.
2. Hardware Layer — Unique Hardware IDs per VM
Every VM receives an independent hardware identity: a randomized MAC address using real vendor OUIs, a disk serial, a mainboard UUID, a realistic machine name and plausible CPU/RAM counts — enough to defeat hardware fingerprint systems such as ThreatMetrix or Akamai that even scan the local network and DNS suffix.
3. Browser Layer — Synchronized Browser Fingerprint
The final layer makes the browser fingerprint match the spoofed hardware: timezone aligned with the proxy, Canvas/WebGL returning a plausible GPU, and WebRTC leaking nothing. This is where a pure VM and an antidetect browser are usually combined.
Antidetect VM vs Antidetect Browser: Which One Should You Choose?
| Criteria | Antidetect VM | Antidetect Browser |
|---|---|---|
| Isolation level | Entire OS + hardware | Browser only (50+ parameters) |
| Account count | 1–5 accounts per VM (maximum safety) | Hundreds of profiles on one machine |
| Deep detection resistance | Survives OS-level and LAN-level scans | Strong fingerprints but OS-level footprints remain |
| Resources | 2–4GB RAM + 20–50GB disk per VM | Lightweight, runs many profiles in parallel |
Quick verdict: up to 5 accounts needing maximum safety → choose an antidetect VM. Scaling to hundreds of profiles → use an antidetect browser. For the hardest platforms (Amazon, eBay, Mercari, online banking) the optimal strategy is hybrid: each VM runs one group of browser profiles.
5 Most Common Antidetect VM Use Cases
- E-commerce multi-accounting — manage multiple Amazon/eBay/Etsy stores without cross-linking.
- Affiliate marketing — run multiple ad accounts, partner accounts and email outreach safely.
- Crypto airdrops & Web3 — each wallet/account in its own isolated environment to avoid sybil filters.
- SEO & SERP tracking — check search results per country without personalization.
- Security testing & malware analysis — an isolated environment for analyzing malware or testing anti-fraud systems.
How to Set Up an Undetectable Virtual Machine (Step by Step)
- Install VMware and create a fresh Windows 10/11 VM without VMware Tools.
- Disable virtualization signals in the
.vmxfile: hide the hypervisor bit, remove the vendor string, disable backdoor I/O and reflect SMBIOS to the host. - Change all hardware IDs: a new MAC address (no VMware OUI), disk serial, mainboard UUID and machine name.
- Attach a dedicated residential/ISP proxy to each VM — the most important layer, because datacenter IPs are blocked instantly no matter how good the fingerprint is.
- Test the fingerprint with Canvas/WebGL/WebRTC checkers; make sure timezone and language match the proxy.
- Use a dedicated browser per VM and never log into the same account across environments.
Note: always comply with each platform's terms of service and the laws where you operate. Antidetect VMs should only be used for legitimate business and security testing.
Frequently Asked Questions
Why is my virtual machine detected by websites?
Because VMware leaks many traces: the "VMwareVMware" CPUID string, SMBIOS vendor names, the 00:0C:29 MAC prefix, VMware Tools processes and the virtual GPU in Canvas/WebGL. A single signal is enough for a system to flag your environment.
Can websites detect VMware?
With default settings — yes; modern anti-fraud systems detect it almost instantly. After a full anti-detection configuration (hidden hypervisor + hardware spoofing + clean fingerprint), the pass rate improves dramatically.
Is an antidetect browser safer than a virtual machine?
Not necessarily. A browser only spoofs fingerprints inside the browser, while a VM spoofs the entire operating system and hardware. For platforms with deep scans (ThreatMetrix, Akamai, banking), an antidetect VM is still the safer choice for a small number of accounts.
Do I need a proxy for an antidetect VM?
Absolutely. Each VM needs its own residential/ISP IP, stable (sticky) and located in the same country as the VM's timezone. The IP is the first layer every platform checks.
Conclusion
The antidetect VM is the strongest anti-detection solution today when you need to run a small number of accounts with maximum isolation — surviving even the deepest checks by hiding the entire virtualization layer instead of only spoofing fingerprints. Combined properly with a residential proxy and an antidetect browser inside, you get a multi-account infrastructure nearly indistinguishable from real users.
Ready to start with a pre-configured undetectable VM? Check DogAnty pricing, read the detailed setup guide or download the trial today.